Knowledge Base
Document
Description
Updated
Global Payouts — Dependency MapStatus: Living reference · Globalized Commerce settlement layer Scope: How an agentic purchase gets from authorized to money-in-a-bank, per market, and what each market depends on.2026-06-21 The Trust FrameworkYou don't have to trust it. You have to be able to check it. Eight practices that make AI-assisted work defensible — free to adopt, no purchase required.2026-07-27
Globalization — Goal Checklist (Pending / Review State)Status board for the globalization parameters of the chat-commerce platform (chatbot, Knowledge Base, market storefronts). Each entry is a goal with its current state. States:2026-06-12
Your Software Investment Is the Barrier to AI EnablementTech debt, redefined: legacy tech that can't convert to the JSON shape AI, Google, and Shopify now run on — verified against Feedonomics, Rithum, and JDA/Blue Yonder documentation.2026-07-13
 From Wayfair to AI Agents — The Road to Machine-Readable CommerceHow South Dakota v. Wayfair (2018), a decade of EU enforcement against Google, and Shopify's Markets architecture (Horizon, GraphQL, Catalogs) converge on one rule: commerce compliance follows the buyer's context — and AI agents now read that context literally. Why i18n, accessibility, and machine-readability are the same plumbing; why semantic components beat compiled utility CSS as LLM context; and how design and content privacy work when the machine plane is an egress channel.2026-07-24
Global compliance harness checklist: test-driven, AI-assistedA checklist for a test harness that blocks a release when a consent, privacy, payment, residency or catalog rule fails. Each item is a test to write before the code: the rule, the kind of test, and the tool — static check, unit, integration, or end to end with Playwright or Selenium.2026-09-30
Served, stored, subpoenaed — sovereign edge serving for KoreaSovereignty is three questions, not one: where a page is served, where the record lives, and whose law can compel it. PIPA's entrustment / provision / cross-border split, what Webflow, Cloudflare and Naver each actually offer, and the crossing inventory that makes a suspension order survivable.2026-09-21
The AI Dialog — Terms for Designers and BAsThe context nobody hands you: silent failure, event bus, hydration, judgment and its six parameters, mandates, privacy streaming — defined plainly, for the people who ship the work.2026-08-03
The Compliance Calendar — 2018 to 2027Every dated obligation shaping commerce data — all public record — and what it obliges of builders: dependency registers, signed non-destructive releases, test loops that keep their verdicts, and proportional review for security that takes no custody.2026-08-06
CRM Sync — Security & Compliance PostureEncrypted per-tenant credentials, scoped revocable tokens, fail-closed consent, offline-verifiable agent mandates, and a public, dated list of open findings.2026-08-16
 CRM Sync — Security Audit & Paired Data RequirementsDate: 2026-05-18 Version: 1.1 Worker Version: dac8f178-f6ed-4a11-96be-f640a67c64ae2026-05-26
Shopify Expiring Token ManagementAs of April 2026, Shopify mandates that all OAuth apps use expiring offline access tokens with rotation. Non-expiring tokens return 403: Non-expiring access tokens are no longer…2026-05-26
Key Ceremony — Loop Review Checklist (Automation)Version: 1.0 Date: 2026-06-22 Companion to: KEY-MANAGEMENT-LIFECYCLE.md (§8 rotation, §9 ceremony, §10 glossary, §12 ownership) Run mode: recurring automated review (e.g. Claude…2026-06-22
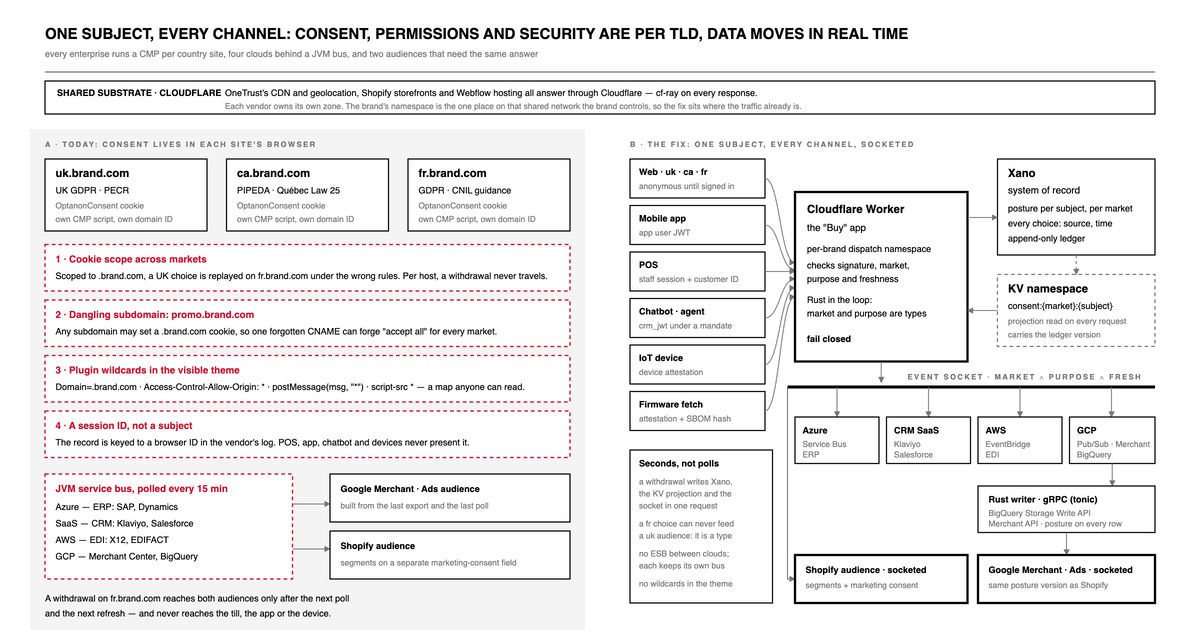
Entitlement SecurityUpdated for php2shell (CVE-2026-109618/109619): patch PHP and keep Cloudflare's WAF rules in Block. Where the vulnerability lives — firmware, game bundles, 3D/BIM assets, the parser that opens them — with Rust in the loop, four cloud data transports, AI task binding, and one subject across every channel: Xano as the record, Cloudflare as the gate.2026-10-21
 BIM Fortress vs Event-SocketTwo diagrams: the fortress wound map and the event-socket heal — envelope encryption, healing encryption, evidence ledger, AI robots on mandates. A+-respectful for Trimble estates: you need more, not different.2026-07-18
Paired permissions and grant impact on machine endpointsWhat read actually grants on a SaaS API, an IPFS CID, an attested device and an edge cache — and what you can still take back from each.2026-09-10
Consent gate attestation — crm-sync.dev, 2026-09-08What the storefront sent before the visitor decided, measured before and after a fix, with the release ids and signed ledger records needed to check the claim independently. A self-attestation with verifiable evidence, not a third-party certification2026-09-08
HAR permissions audit — a portable prompt for testing an e-commerce storefrontHand this file and a HAR capture to any AI assistant and get a permissions audit of your own storefront: what the server actually returned versus what the page displayed, whether the consent gate resolved before the tags fired, credentials reaching t2026-09-07
Security & Privacy — Questions from CISOs and DPOsThe questions a security or privacy office would ask if we weren't in the room — including the ones we'd rather they didn't. Open findings, with dates, at the bottom.2026-07-14
CRM Sync — Key Management LifecycleVersion: 1.5 Date: 2026-07-03 (v1.4: 2026-06-22; v1.2: 2026-06-15; v1.1: 2026-06-11; v1.0: 2026-05-26) Scope: Dev → Stage → Prod key management, consulting team workflow, stakeh…2026-07-03
CRM Sync — Auth PipelinesFor: Engineering, security auditors, and compliance teams reviewing authentication architecture Date: 2026-05-192026-05-29
Keys to the Castle with Design Ops ToolsDistributed entitlement built with Design Ops tools - Webflow, Xano and Cloudflare - mapped feature by feature against Vault and Consul. Same utility, same security, same scaling. Plus minting: an artifact a customer can be granted, which a secrets engine was never built to hold.2026-08-16
Agent Authority — Technical BriefFor teams already running agent workflows: per-agent mandates with scope, cap and expiry; authority resolved per call rather than at the boundary; MCP with scoped tokens; and offline verification against a published Ed25519 key.2026-07-27
AI cross-border requirements: a scannable checklistWhat an AI service that moves personal data across borders must guarantee — data governance, transport, horizontal scaling, AI-specific controls — mapped to the SOC 2 Trust Services Criteria, with the evidence a reviewer asks for; plus US middleware fees and the retention, consent and retargeting gaps that turn into penalties.2026-09-25
CRM Sync — Firmware, SBOM & the Cyber Resilience ActWhat an SBOM is, what firmware vaulting does, and how the EU Cyber Resilience Act maps onto both — plus a glossary of the security terms (envelope encryption, hash-chained ledger, grant-gated download, CORS, nosniff).2026-07-20
Cybersecurity for AI — CISO · CTO · DPOWhat the EU Cyber Resilience Act requires, what firmware and SBOMs are, why CISOs, CTOs, and DPOs are personally exposed when a system only looks like it works, the billion-dollar GDPR precedent behind the server-side migration, and two pathways to compliance: bundled-AI SaaS vs. AI-as-middleware.2026-07-25
Entitlement Strategy — RBAC, ABAC, RuBAC & Permissions for AI AgentsHow RBAC, ABAC, and RuBAC actually relate; why WordPress roles, AWS IAM, and Azure RBAC stop at the door; and how an entitlement plane with purchase-granted capability caps, envelope encryption, and AP2 mandates gates AI agents.2026-07-20
Org Trust Layer: Your Own CA, Fewer PluginsYour own certificate authority and signing keys: machine identity, signed consent and provenance, a signed SAP document count, and fewer plugins.2026-10-29
Ownership before the wire: a per-country rules ladder for AI, functions and formsMost forms, ERPs and CRMs predate Rust and today's privacy law, so they shape the record first and filter it later. Rules owned per country, published as tested artifacts, and AI agents and functions that get a data binding only when a mandate resolves.2026-10-09
Permissions for AI, in plain terms — capability, not perimeterPermissions for AI agents in plain 1-2-3: RBAC/ABAC/RuBAC/OIDC/OAuth defined, why RBAC breaks for AI, and five real-world proofs (household streaming, HIPAA 3D printing, private mortgage, dark-warehouse robots on GS1 QR Sunrise 2027, geo-verified BIM inspection). Money- and privacy-gated.2026-08-09
PHP Commerce: Moving Off Shared HostingFamiliar is not the same as safe. After the October 2026 delistings and checkout hijack: what WordPress, WooCommerce, Magento and PHP-backed Shopify apps move to, in what order, and what it costs. PDF edition available.2026-10-22
 QA and Release Gating for Agents, Mandates and RobotsWhat changes in a test suite when the caller is an agent or a machine with an actuator — adversarial refusal tests, a gate that fails closed, and what SRI actually protects.2026-09-20
Rotate a Key in Three Steps — the AI-Safe Ceremony for Webflow TeamsWebflow and Shopify have no native key rotation — a token is one static secret. Demote platform tokens to plumbing; put people, agents, and permissions on paired entitlement that rotates with named generations.2026-07-29
Secure frontend, AI-safe backend: Webflow collections, fallback publishing and grantsHow a Webflow site published as static files pairs each publishing step with a permission: collections as MVC, fallbacks that fail toward less exposure, review switches as publish grants, and where TLS, memory safety and authorization fit.2026-10-04
Security Reinforcement: Firmware Asset PublishingTooling, a UAT plan whose cases are meant to fail the install, and what a shipped secret is worth — because TLS proves the connection, not the bytes.2026-09-20
Server-Side or It Didn't Happen — Developer Due DiligenceA theme that looks right is not a system that is right: shape-gated server functions, the consent register, the three-surface demonstration — and who carries what you didn't write down.2026-08-05
SOC / SOX Application Review — AI Middleware, Reinforced Security, Data ScalingThe application-review checklist across the four IT General Control domains plus AI requirements and dependency/failover — and why the foundation holds: AI as free-to-use middleware, security reinforcement that fails closed, and data scaling on one session-keyed ledger, with SOC-aligned controls built in rather than bolted on.2026-07-25
The BYO data plane fallback ladder: whose warehouse, and what erasure does to itWhen a tenant brings its own Xano and BigQuery, every write has to land in the tenant's warehouse, and every erasure has to respect the tenant's choice. The five-rung ladder that resolves a tenant's BigQuery project, the operator-approved exceptions and the page that manages them, the tombstone-then-purge erasure and the per-tenant policy for the tenant's own planes, and what Shopify, Google and Klaviyo each do with a deletion2026-09-16
The Trust Vocabulary — Every Term on One PagePermission, privacy, license vs grant, receipt, record of consumption, fingerprint, vault, token vs bookmark, key pair, mandate — one breath each, with who acts on it.2026-07-29
The Wrong-Size Tool — Why Consent Never Lands on a ServerEnterprise IT was built to guard the perimeter; regulators now ask what the servers did. Into that gap walk consulting firms selling platform programs — Salesforce, MuleSoft, ESB rebuilds, WMS replacements — that still never put consent on a server. The ladder runs from scoping failure to material weakness to securities litigation, and the fix that would have protected the organization was nearly free. Why the right-size tool gets dismissed, what a station is versus a destination, and why every high-order function — consent, entitlement, evidence, even the design system — must arch both.2026-07-25
Trust Roots Across CloudsWhat TLS actually buys and where it stops — and why a permission is intent, mandate and policy together, never a token anybody carries.2026-09-09
Trust With Login — The Bind Is the ProductThe login binds accounts you already own; permissions come from the register, not an installed app; eight frontends, one gate; every sign-in is a ledger event.2026-08-06
Two Ways to Give an Agent a KeyParticipant-held (Nostr) vs edge-held Ed25519 key custody for AI agents: identity vs authority, rotation after compromise, decentralized egress under enterprise controls, three-leg resilience, and a 20-term glossary.2026-07-27
Verify It Yourself — the IT SheetOne page, both registers: the four-click demo for the business stakeholder; independent-verification claims, endpoints, and tests for IT.2026-07-29
What Is an SBOM? Who Uses This? Everyone.The LinkedIn edition — question-first: what an SBOM is, who uses it (everyone), and how a regulatory threat became a composable publishing system.2026-07-29
Your Firmware Is a URL — the CRA Assumes an Evidence ChainThe CRA clock as a records problem — SBOMs, vaulting, and the SaaS answer: ledger sessions, not artifacts. With the relay-vs-entitlement contrast.2026-07-29
SVG, Rust and Elm: the security gaps illustrationOne diagram that follows a single SVG file from source to base64 to the browser, through an Elm client, TLS, Cloudflare, Xano and a Rust service, two TLS pipelines, JVM, iPaaS and Wasm stacks, and VM, Docker and Kubernetes isolation — with 31 numbered gaps and their fixes, a second illustration of browser, machine and agent callers, the assumptions that break as a system adds commerce, goes global and becomes AI-legible, how Rust keeps an SVG renderer memory-safe and what it still leaves to limits, how to make an SVG tell a model what it shows a person, and a list of known foot guns.2026-10-19
Design for Secure Revenue ProjectionSecurity as a designed component of the revenue signal path: how conversion values, predicted lifetime value and audiences leave a store's own record for Google, Klaviyo and other channels, what the security component checks at each hop, its states and failure modes, what is built and tested today, and what it costs.2026-10-24
Consent, Cookies & Preferences — User GuideThe consent banner, cookie preferences, reset, Do Not Sell vs consent, and the audit trail.2026-07-09
CRM Sync — Migration Guide: CSV & Legacy Tools → Connected StreamsFor: Marketing ops, analytics teams, and CRM administrators planning the transition Date: 2026-05-182026-05-26
 Agency → Client Deploy HandoffChecklist + Interactive Key Rotation ceremony. This document is the normative handoff procedure for transferring a deployed CRM Sync / headless commerce stack from the implement…2026-06-12
File System Agnostic PublishingShip the Webflow design as a WordPress theme (Udesly or Pinegrow) or on EmDash/Astro — the Shopify Web Components block and CRM Sync embeds carry across verbatim.2026-09-10
How to capture a HAR file — a plain-language guideA HAR file is a recording of every conversation your browser had with a website. This explains what one is, how to capture a useful one in Chrome, Edge, Firefox or Safari, the single setting most people miss, how to check what is inside before you sh2026-09-07
CRM Sync — PWA & Native App Commerce Setup ReferenceShip your CRM as an installable PWA and native app (iOS · Android · desktop) on Shopify + Webflow + Xano — with auth, real-time consent, GA4, and agent permissions. Everything you need to get it running, in order.2026-07-06
CRM Sync Setup ReferenceThe full technical reference for the CRM Sync stack. New users: start with the short numbered guide at crm-sync.dev/start — this page is for depth.2026-07-07
Logging and trace fees: what monitoring costs by volumeLog entries and trace spans are the two monitoring lines that grow with traffic rather than with tenants. What Google Cloud Logging, Cloud Trace and Cloud Monitoring charge, what Cloudflare Workers Logs and Traces charge from 1 October 2026, what a fixed-fee Xano plan leaves out, and the four settings that decide the bill before the first invoice does2026-09-16
Marketing was built on the page view. The funnel now pays for the consented login.For: Marketing ops, performance media, and analytics engineering Status: Built (GA4 push + audiences) · Direct Google Ads push pending Ads API credentials Date: 2026-07-07 Depen…2026-07-22
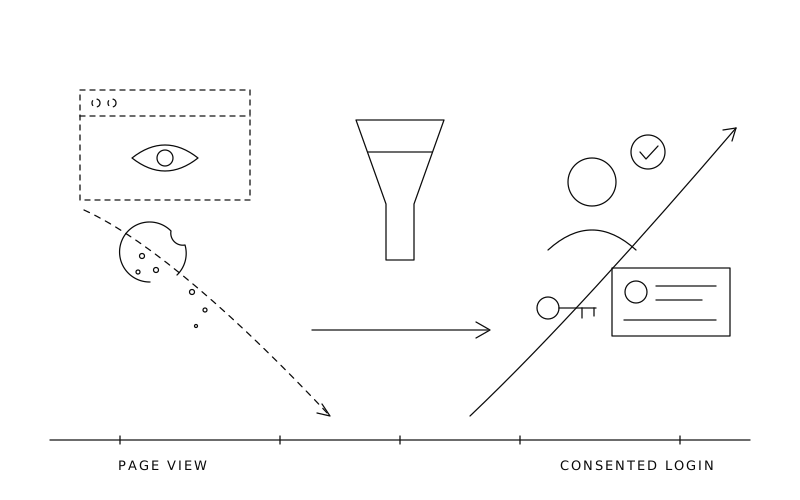 Google turned off the list upload. We were never uploading lists.For: Marketing ops, analytics engineering, and the business analyst who owns segments Status: Plan of record · GA4 pipe built · Live Google push routes via the Data Manager API2026-07-10
Shopify App Requirements Checklist (2026)A comprehensive, downloadable checklist for building, submitting, and maintaining a Shopify App Store app. Based on Shopify's official App Store requirements and the latest plat…2026-05-29
 CRM Sync — Shopify App Platform ChangesFor: Product managers, operations teams, and business stakeholders tracking Shopify app compliance Date: 2026-05-182026-05-26
Risk & Liability Brief — The 2026 Client-Side CliffAudience: owners, finance, legal, and engineering leads who carry the downside. As of: 2026-06-21 · Companion to: FORWARD-DEPLOY-AGENTIC-GRAPHQL.md (the fix).2026-06-21
Dawn → Horizon: Agentic Cart FunctionsMove client-side Dawn logic to server-side Functions and the Tool Runner — agent-driveable under an AP2 mandate. Includes the Scripts→Functions map and the dated migration checklist.2026-08-06
Hydrogen or a Bespoke Xano + Cloudflare StackShopify Hydrogen 2026-10 compared with a bespoke Xano + Cloudflare stack: integrations, the Shopify and Google deprecation calendar, sign-in, agent checkout, wallets, apps, 3D and permissions.2026-10-29
REST Is Not GraphQLWhat actually breaks when a Shopify integration moves from REST to GraphQL: the inverted error model, cost-based rate limiting, GID identifiers, cursor pagination, and unequal surface coverage - with the failure mode each produces and an audit checklist.2026-07-27
Shopify and Google sunsets: what is due before 11 November 2026Every Shopify, Google Analytics and Google Ads deprecation dated between 16 September and 11 November 2026, the five topics merchants ask about — native mobile, short-lived tokens, the REST sunset, GraphQL data layers, and GA4 consent and conversions — and whether CRM Sync is exposed to each, with every source linked.2026-09-16
JS Execution Order — Challenge & SolutionConsent fires first: the client-JS execution-order contract and the tests that enforce it.2026-07-09
AI Trust Framework RequirementsTen requirements an AI trust framework must satisfy, why REST integration cannot meet them by default, and nine additive changes that close the gap without rewriting an endpoint.2026-07-27
CRM Sync — Why This Architecture Is SaferFor: Business leaders, compliance officers, and operations teams evaluating CRM Sync Date: 2026-05-182026-05-26
 Process Management Guide — Webflow · Xano · Cloudflare · ShopifyFour-platform resilience: layer split, event-driven automation, outage runbook and RACI - now extended with verification evidence, SBOM/CRA obligations and AEO surfaces.2026-07-27
Server-Side Function Tools with AI RunnersThe additive way into an enterprise stack: bounded functions that resolve authority per call, record themselves, and give an AI runner capability without a migration to own.2026-07-27
CRM Sync — UI Component & ID RegistryCanonical naming + delivery model for the storefront UI system (nav, footer, cart, login, search) across design-sync.myshopify.com → crm-sync.dev. One addressable crm- namespace…2026-07-07
Product Taxonomy, GraphQL and the GID RenameCPG planning toward Sunrise 2027: what changes when product identity moves into a typed graph with GID identifiers - the parent/child collision, the silent join breakage, and the five identifiers an item master has to carry.2026-07-28
CRM Sync — Feature SpecificationDocument ID: CRM-FEAT-003 Version: 1.0 Date: 2026-07-06 Status: Published Classification: Public Parent: CRM-FUNC-SPEC-0012026-07-06
Forward-Deploy Guideline — Server-Side GraphQL + Agentic Workflows + Tool RunnerAudience: merchants, app developers, and platform teams planning their Shopify roadmap. Thesis: Shopify's 2025–2026 deprecation cliff retires the client-side / REST / Script-Edi…2026-06-21
CRM Sync — What Traditional CRMs MissFor: Business leaders, investors, and operations teams evaluating CRM Sync against Salesforce, HubSpot, and Klaviyo Date: 2026-05-192026-07-19
Analytics Export via Xano Polling + Worker CronVersion: 1.0 Date: 2026-05-27 Status: Specification2026-05-27
Consent-first tracking and the demotion of page and client dataFour dated platform moves demoted the page view from record to hint. Requirements and risk for the theme, what agentic conversion needs instead, and where the page view is still right — AEO vs SEO.2026-09-10
CRM Sync — Functional SpecificationDocument ID: CRM-SYNC-FUNC-SPEC-001 Version: 1.0 Date: 2026-07-12 Status: Active Classification: Public2026-07-12
CRM Sync — Feature Specification AddendumDocument ID: CRM-FEAT-002 Version: 1.0 Date: 2026-05-17 Status: Draft — Architecture Review Parent: CRM-FUNC-SPEC-001 v1.22026-06-25
AI enabled forms with LLM weighting — one form, many outcomesOne form, many outcomes: the business case against CRM latency, per-contact fees and vendor lock-in, with sprint directives and why a claim's shape decides what an AI can be asked.2026-09-08
Asset Management, Security and AIA media manager's pipeline — metadata and provenance, raster and mesh compression, programmatic resize, and the four places media can live compared on egress.2026-09-20
BYO Shape PipelineBring your own Xano, Kubernetes and LLM to the shape pipeline — the merge contract, the write path, the entitlement gate, and a dependency table where every row is self-serve.2026-09-09
BYO Xano and BigQuery against Google's agent platform: what AI automation costs per callGoogle's agent platform is the faster way to build an AI automation, and its managed layers bill every request. What Conversational Agents, Agent Search, grounding and Agent Runtime charge per call, what the same jobs cost on a bring-your-own Xano and BigQuery stack with Cloudflare Workers AI, where Google is cheaper, and the price changes dated between now and January 20272026-09-16
Claim Provenance — the metadata schemaEvery document here is CC BY 4.0. This defines the metadata that travels with it — what was checked, how it was checked, when, and when it should be checked again.2026-09-04
Compile to update — the estate by seven lifecycle stagesEvery application against the same seven stages: compile, permissions, render, bundle, deploy, version, update. The empty cells are the informative ones.2026-09-07
Consent Resolution on Higher-Order LoadThe five-phase load contract that resolves consent from durable state before any tag loads — portable to any client-side template, device- and browser-agnostic.2026-09-04
Decision ladder — functional and data design spec (hypothetical)A support chatbot that climbs from knowledge-base answers to opening a return, escalates to a person on named conditions, links only attested firmware and deploys only through a locked, human-reviewed workflow. With a test matrix.2026-10-04
Fragments on Any Frontend — One Webflow Source, Every PlatformSections authored once in Webflow mount verbatim on AEM, WordPress, Astro, Next, 11ty, or a Shopify theme — markup travels, behavior never does.2026-08-03
From Plugins to MandatesWhy per-seat pricing taxes the automation you bought it for, what each external DAM, PIM and CRM adds to supply chain risk, and why vendor JSON is the wrong shape for an agent.2026-09-20
Git to Every Surface — the Article PipelineOne markdown commit becomes a Webflow article, a Shopify metaobject, and an AEM Content Fragment — with hashtags as the filter dimension and ALT text carried from the source.2026-08-11
Middleware vs AI ArchitectureWhy a Xano record plus a Cloudflare edge resolves identifier and consent drift that VM-hosted middleware cannot, what a GTIN check digit proves, and where cryptographic trust sits in a Channel Publish QR link.2026-10-17
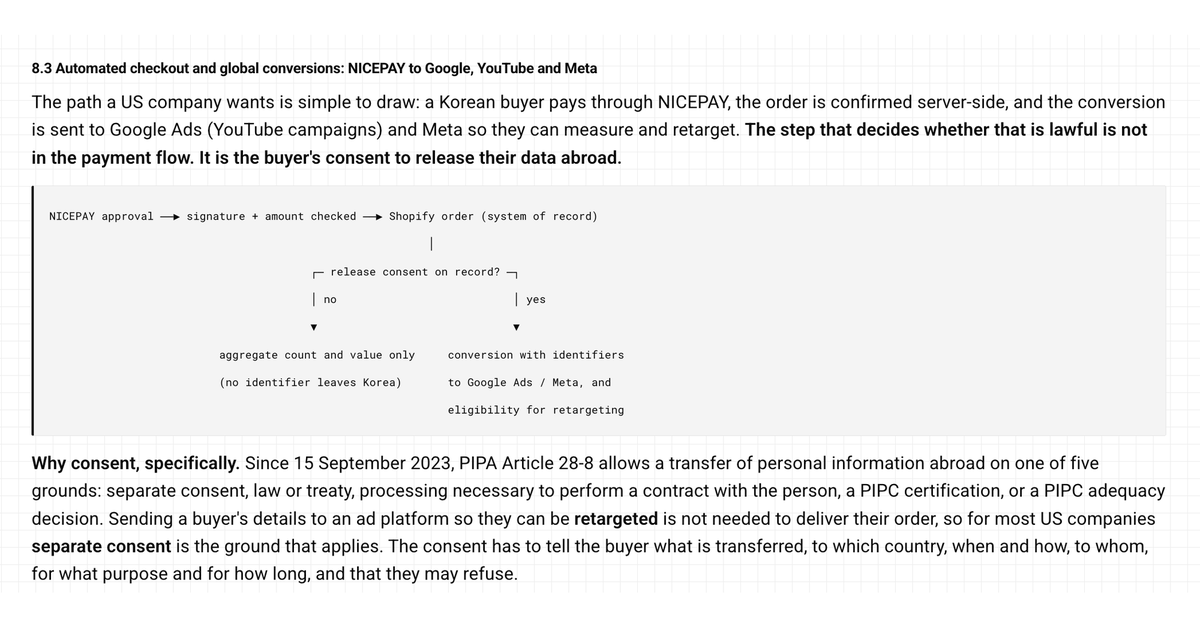
October 1: script tags, Functions, the cart, the catalog agents read — Globalized Language ISO requirementsWhat server-side consent buys globally: the three-year conversion from browser tags to Consent Mode v2 (September 2023 to March 2027), what Google, Meta and the law require, and why no session-level consent log means no YouTube or Meta retargeting; a real-time consent log, California's Honda and Todd Snyder fines, and the browser opt-out signal from 1 January 2027; business-as-usual data vs an API-reinforced global namespace, from market-prefixed domains to Cloudflare Rules; a retire and adopt checklist; then Shopify's 1 October 2026 script tag deadline, Functions, what is reserved in cart and checkout, the ISO standards of the UCP catalog, and Korea's NICEPAY and consent path.2026-09-30
 PIM Anywhere — One Catalog Record, Any FrontendOne live catalog record projected onto any frontend — AEM, Webflow, WordPress, Next — via a two-tag embed; the same record ships to Google through the Merchant API.2026-08-05
Render and Runtime: A Working DictionaryISR, islands, HTMX against Next.js, Liquid, PHP passthrough, Deno against Node, keys against cookies, UAT, adversarial testing and SRI — each defined by the decision it changes.2026-09-20
Shopify / Google Integration on an AEM Scaffold — via Webflow ExportThe Webflow export as the AEM page scaffold, worker embeds as the behavior layer, and the either/or substrate election — beside AEM, never inside it.2026-08-02
The AI ladder: retrieval, adapters, humans, and who holds the keysChallenge and solution for putting AI into commerce without letting it decide what it may not. Definitions of RAG, CRAG, LoRA and human-in-the-loop escalation; when data justifies each rung; and why ADK, Kubernetes/Helm and a Cloudflare higher-order 'helmet' are three different layers — with the mandate as the only way an agent is allowed to act; and what a SOC 2 review — a procedural assessment of how an organisation operates, not a certification — asks of AI transport.2026-09-25
The spec is the source — a writing layer for designers and analystsConfiguration files are the specification. Write the intent in plain language, generate the config, and get the developer and compliance documentation from the same file.2026-09-07
Why Xano + AI + e-commerce is the right runtime as a serviceA runtime is judged by what it holds when nothing is being rendered. The identity path across Shopify OIDC, a worker and Xano; a consent gate that is metered rather than loaded; and why Supabase and Firebase lost on the enforcement point.2026-09-06
CRM Sync — Clean Room Utility & Security RulesVersion: 1.1 — Cloudflare-Native Architecture Date: 2026-05-27 Classification: Internal — Confidential Compliance: GDPR Art. 6/9, CCPA §1798.140, CPRA, UK DPA 2018 Infrastructur…2026-05-27
GUIs when you still ship JavaScript: Webflow, Elm, Javy, Tauri and Rust down to machine codeA field guide to interface options for a stack that keeps its JavaScript and TypeScript: Webflow with TypeScript embeds and Workers side by side, Elm and SVG islands, Shopify Functions compiled from JS with Javy, Rust in the browser through WebAssembly, Tauri around an existing web UI, native Rust GUIs (iced, egui, Slint), and no_std firmware with no GUI at all — compared by what JavaScript remains at runtime and where trust is enforced.2026-10-12
From product.csv to Consented ConversionsGoogle retired the Content API and Amazon now drops conversions with no consent signal. Why a product.csv data layer can no longer feed ads or measurement, how a connected ERP, CRM and PIM replace it, and an eighteen-item checklist with a downloadable test harness.2026-10-19
Consented data layer test harnessEighteen tests that prove a catalog has moved off a product.csv data layer: feeds on current APIs, identifiers joined by key, consent attached to every conversion, and a clean boundary between the PIM and the CRM. Each test is a shell check, an in-app check or a browser check, with the result that counts as a pass.2026-10-19
Hyperscaler vs Distributed: Webflow, Xano and Cloudflare Decision LaddersWhere compute should live, from hyperscalers and GPU neoclouds to edge networks. Opens with task runners, data bindings, and GPUs as a rented place (CoreWeave, Oracle OCI) versus GPU code compiled from Rust to bytecode. Then the frame-budget origin: how game engines already ration the GPU, why C and C++ renderers such as Flash and SVG parsers forced isolation that Rust and Wasm remove, how Shopify Functions already run Wasm as a security boundary inside checkout, and the Rust path for new work: a Webflow page, a Cloudflare compile and a Xano record. Then the strategy: bind before you allocate, with the cost and security case for running distributed data and AI binding before any GPU is allocated. Then incremental knowledge against general-purpose AI: evidence weighting, ranking, and falling back to a larger token model only when the ranked data can't answer. Then context and data streams that scale by direction before intent is tokenized or vectorized. Then why Kubernetes and VMs limit reach but not what a model may weigh, how AWS, Google Cloud and Azure each control data moving between workloads, what an enterprise has to add on top, and policy management as a service: rules authored in Webflow and Xano, enforced by Cloudflare above every cloud, worked through one order that reaches Salesforce and Klaviyo on AWS, SAP or Dynamics on Azure, Google Ads on Google Cloud and a Shopify Function; and one Worker behind any theme, a Webflow export or a Shopify theme through the App Proxy, with an allowlist that mirrors Kakao Pay's registered domains; a sandbox that restricts outside data before it reaches on-prem; and why an AI strategy is not a JVM: security for AI as permissions as architecture, with the stack and the heap as a model for which data and grants may outlive a call; immutable and dynamic data in KV; claims and extras as layered permissions for people; and why a one-domain consent banner such as OneTrust has to fold into the data design that AI services read. Then two decision ladders, for orchestration and for AI binding, across Webflow, Cloudflare and Xano, plus what each rung does to residency, latency, cost, audit scope and failure modes in enterprise infrastructure.2026-10-20
CRM Sync — Event-Driven Integration SpecVersion: 1.0 Date: 2026-05-27 Status: Specification Replaces: Cron-only polling for external integrations2026-07-22
Webflow App Requirements Checklist (2026)A comprehensive, downloadable checklist for building, submitting, and maintaining a Webflow Marketplace app. Based on Webflow's official Marketplace guidelines and the latest pl…2026-05-29
 Design HelmetThe Helmet is our way of drawing the logo once so that every site colours it automatically to match the brand — you never re-export it, and you never touch code.
Safe SVG for Webflow and UIkitAn img is sandboxed; inlining spends that sandbox for stylability. An allow-list sanitiser buys it back — tested against twelve vectors, with GSAP and Lottie separated by who supplies the program.2026-09-20
The Webflow App Stack — Vite + TypeScript Monorepo, with 11ty/Vue/Svelte IslandsThe modern hybrid-app scaffold: pnpm monorepo, Vite + TS extension, CF Worker, shared types end-to-end — plus 11ty/Astro islands for the site and the Turbopack risk, defined.2026-07-29
The Trust FrameworkYou don't have to trust it. You have to be able to check it. Eight practices that make AI-assisted work defensible — free to adopt, no purchase required.2026-07-27
Globalization — Goal Checklist (Pending / Review State)Status board for the globalization parameters of the chat-commerce platform (chatbot, Knowledge Base, market storefronts). Each entry is a goal with its current state. States:2026-06-12
Your Software Investment Is the Barrier to AI EnablementTech debt, redefined: legacy tech that can't convert to the JSON shape AI, Google, and Shopify now run on — verified against Feedonomics, Rithum, and JDA/Blue Yonder documentation.2026-07-13
From Wayfair to AI Agents — The Road to Machine-Readable CommerceHow South Dakota v. Wayfair (2018), a decade of EU enforcement against Google, and Shopify's Markets architecture (Horizon, GraphQL, Catalogs) converge on one rule: commerce compliance follows the buyer's context — and AI agents now read that context literally. Why i18n, accessibility, and machine-readability are the same plumbing; why semantic components beat compiled utility CSS as LLM context; and how design and content privacy work when the machine plane is an egress channel.2026-07-24
Global compliance harness checklist: test-driven, AI-assistedA checklist for a test harness that blocks a release when a consent, privacy, payment, residency or catalog rule fails. Each item is a test to write before the code: the rule, the kind of test, and the tool — static check, unit, integration, or end to end with Playwright or Selenium.2026-09-30
Served, stored, subpoenaed — sovereign edge serving for KoreaSovereignty is three questions, not one: where a page is served, where the record lives, and whose law can compel it. PIPA's entrustment / provision / cross-border split, what Webflow, Cloudflare and Naver each actually offer, and the crossing inventory that makes a suspension order survivable.2026-09-21
The AI Dialog — Terms for Designers and BAsThe context nobody hands you: silent failure, event bus, hydration, judgment and its six parameters, mandates, privacy streaming — defined plainly, for the people who ship the work.2026-08-03
The Compliance Calendar — 2018 to 2027Every dated obligation shaping commerce data — all public record — and what it obliges of builders: dependency registers, signed non-destructive releases, test loops that keep their verdicts, and proportional review for security that takes no custody.2026-08-06
CRM Sync — Security & Compliance PostureEncrypted per-tenant credentials, scoped revocable tokens, fail-closed consent, offline-verifiable agent mandates, and a public, dated list of open findings.2026-08-16
CRM Sync — Security Audit & Paired Data RequirementsDate: 2026-05-18 Version: 1.1 Worker Version: dac8f178-f6ed-4a11-96be-f640a67c64ae2026-05-26
Shopify Expiring Token ManagementAs of April 2026, Shopify mandates that all OAuth apps use expiring offline access tokens with rotation. Non-expiring tokens return 403: Non-expiring access tokens are no longer…2026-05-26
Key Ceremony — Loop Review Checklist (Automation)Version: 1.0 Date: 2026-06-22 Companion to: KEY-MANAGEMENT-LIFECYCLE.md (§8 rotation, §9 ceremony, §10 glossary, §12 ownership) Run mode: recurring automated review (e.g. Claude…2026-06-22
Entitlement SecurityUpdated for php2shell (CVE-2026-109618/109619): patch PHP and keep Cloudflare's WAF rules in Block. Where the vulnerability lives — firmware, game bundles, 3D/BIM assets, the parser that opens them — with Rust in the loop, four cloud data transports, AI task binding, and one subject across every channel: Xano as the record, Cloudflare as the gate.2026-10-21
BIM Fortress vs Event-SocketTwo diagrams: the fortress wound map and the event-socket heal — envelope encryption, healing encryption, evidence ledger, AI robots on mandates. A+-respectful for Trimble estates: you need more, not different.2026-07-18
Paired permissions and grant impact on machine endpointsWhat read actually grants on a SaaS API, an IPFS CID, an attested device and an edge cache — and what you can still take back from each.2026-09-10
Consent gate attestation — crm-sync.dev, 2026-09-08What the storefront sent before the visitor decided, measured before and after a fix, with the release ids and signed ledger records needed to check the claim independently. A self-attestation with verifiable evidence, not a third-party certification2026-09-08
HAR permissions audit — a portable prompt for testing an e-commerce storefrontHand this file and a HAR capture to any AI assistant and get a permissions audit of your own storefront: what the server actually returned versus what the page displayed, whether the consent gate resolved before the tags fired, credentials reaching t2026-09-07
Security & Privacy — Questions from CISOs and DPOsThe questions a security or privacy office would ask if we weren't in the room — including the ones we'd rather they didn't. Open findings, with dates, at the bottom.2026-07-14
CRM Sync — Key Management LifecycleVersion: 1.5 Date: 2026-07-03 (v1.4: 2026-06-22; v1.2: 2026-06-15; v1.1: 2026-06-11; v1.0: 2026-05-26) Scope: Dev → Stage → Prod key management, consulting team workflow, stakeh…2026-07-03
CRM Sync — Auth PipelinesFor: Engineering, security auditors, and compliance teams reviewing authentication architecture Date: 2026-05-192026-05-29
Keys to the Castle with Design Ops ToolsDistributed entitlement built with Design Ops tools - Webflow, Xano and Cloudflare - mapped feature by feature against Vault and Consul. Same utility, same security, same scaling. Plus minting: an artifact a customer can be granted, which a secrets engine was never built to hold.2026-08-16
Agent Authority — Technical BriefFor teams already running agent workflows: per-agent mandates with scope, cap and expiry; authority resolved per call rather than at the boundary; MCP with scoped tokens; and offline verification against a published Ed25519 key.2026-07-27
AI cross-border requirements: a scannable checklistWhat an AI service that moves personal data across borders must guarantee — data governance, transport, horizontal scaling, AI-specific controls — mapped to the SOC 2 Trust Services Criteria, with the evidence a reviewer asks for; plus US middleware fees and the retention, consent and retargeting gaps that turn into penalties.2026-09-25
CRM Sync — Firmware, SBOM & the Cyber Resilience ActWhat an SBOM is, what firmware vaulting does, and how the EU Cyber Resilience Act maps onto both — plus a glossary of the security terms (envelope encryption, hash-chained ledger, grant-gated download, CORS, nosniff).2026-07-20
Cybersecurity for AI — CISO · CTO · DPOWhat the EU Cyber Resilience Act requires, what firmware and SBOMs are, why CISOs, CTOs, and DPOs are personally exposed when a system only looks like it works, the billion-dollar GDPR precedent behind the server-side migration, and two pathways to compliance: bundled-AI SaaS vs. AI-as-middleware.2026-07-25
Entitlement Strategy — RBAC, ABAC, RuBAC & Permissions for AI AgentsHow RBAC, ABAC, and RuBAC actually relate; why WordPress roles, AWS IAM, and Azure RBAC stop at the door; and how an entitlement plane with purchase-granted capability caps, envelope encryption, and AP2 mandates gates AI agents.2026-07-20
Org Trust Layer: Your Own CA, Fewer PluginsYour own certificate authority and signing keys: machine identity, signed consent and provenance, a signed SAP document count, and fewer plugins.2026-10-29
Ownership before the wire: a per-country rules ladder for AI, functions and formsMost forms, ERPs and CRMs predate Rust and today's privacy law, so they shape the record first and filter it later. Rules owned per country, published as tested artifacts, and AI agents and functions that get a data binding only when a mandate resolves.2026-10-09
Permissions for AI, in plain terms — capability, not perimeterPermissions for AI agents in plain 1-2-3: RBAC/ABAC/RuBAC/OIDC/OAuth defined, why RBAC breaks for AI, and five real-world proofs (household streaming, HIPAA 3D printing, private mortgage, dark-warehouse robots on GS1 QR Sunrise 2027, geo-verified BIM inspection). Money- and privacy-gated.2026-08-09
PHP Commerce: Moving Off Shared HostingFamiliar is not the same as safe. After the October 2026 delistings and checkout hijack: what WordPress, WooCommerce, Magento and PHP-backed Shopify apps move to, in what order, and what it costs. PDF edition available.2026-10-22
QA and Release Gating for Agents, Mandates and RobotsWhat changes in a test suite when the caller is an agent or a machine with an actuator — adversarial refusal tests, a gate that fails closed, and what SRI actually protects.2026-09-20
Rotate a Key in Three Steps — the AI-Safe Ceremony for Webflow TeamsWebflow and Shopify have no native key rotation — a token is one static secret. Demote platform tokens to plumbing; put people, agents, and permissions on paired entitlement that rotates with named generations.2026-07-29
Secure frontend, AI-safe backend: Webflow collections, fallback publishing and grantsHow a Webflow site published as static files pairs each publishing step with a permission: collections as MVC, fallbacks that fail toward less exposure, review switches as publish grants, and where TLS, memory safety and authorization fit.2026-10-04
Security Reinforcement: Firmware Asset PublishingTooling, a UAT plan whose cases are meant to fail the install, and what a shipped secret is worth — because TLS proves the connection, not the bytes.2026-09-20
Server-Side or It Didn't Happen — Developer Due DiligenceA theme that looks right is not a system that is right: shape-gated server functions, the consent register, the three-surface demonstration — and who carries what you didn't write down.2026-08-05
SOC / SOX Application Review — AI Middleware, Reinforced Security, Data ScalingThe application-review checklist across the four IT General Control domains plus AI requirements and dependency/failover — and why the foundation holds: AI as free-to-use middleware, security reinforcement that fails closed, and data scaling on one session-keyed ledger, with SOC-aligned controls built in rather than bolted on.2026-07-25
The BYO data plane fallback ladder: whose warehouse, and what erasure does to itWhen a tenant brings its own Xano and BigQuery, every write has to land in the tenant's warehouse, and every erasure has to respect the tenant's choice. The five-rung ladder that resolves a tenant's BigQuery project, the operator-approved exceptions and the page that manages them, the tombstone-then-purge erasure and the per-tenant policy for the tenant's own planes, and what Shopify, Google and Klaviyo each do with a deletion2026-09-16
The Trust Vocabulary — Every Term on One PagePermission, privacy, license vs grant, receipt, record of consumption, fingerprint, vault, token vs bookmark, key pair, mandate — one breath each, with who acts on it.2026-07-29
The Wrong-Size Tool — Why Consent Never Lands on a ServerEnterprise IT was built to guard the perimeter; regulators now ask what the servers did. Into that gap walk consulting firms selling platform programs — Salesforce, MuleSoft, ESB rebuilds, WMS replacements — that still never put consent on a server. The ladder runs from scoping failure to material weakness to securities litigation, and the fix that would have protected the organization was nearly free. Why the right-size tool gets dismissed, what a station is versus a destination, and why every high-order function — consent, entitlement, evidence, even the design system — must arch both.2026-07-25
Trust Roots Across CloudsWhat TLS actually buys and where it stops — and why a permission is intent, mandate and policy together, never a token anybody carries.2026-09-09
Trust With Login — The Bind Is the ProductThe login binds accounts you already own; permissions come from the register, not an installed app; eight frontends, one gate; every sign-in is a ledger event.2026-08-06
Two Ways to Give an Agent a KeyParticipant-held (Nostr) vs edge-held Ed25519 key custody for AI agents: identity vs authority, rotation after compromise, decentralized egress under enterprise controls, three-leg resilience, and a 20-term glossary.2026-07-27
Verify It Yourself — the IT SheetOne page, both registers: the four-click demo for the business stakeholder; independent-verification claims, endpoints, and tests for IT.2026-07-29
What Is an SBOM? Who Uses This? Everyone.The LinkedIn edition — question-first: what an SBOM is, who uses it (everyone), and how a regulatory threat became a composable publishing system.2026-07-29
Your Firmware Is a URL — the CRA Assumes an Evidence ChainThe CRA clock as a records problem — SBOMs, vaulting, and the SaaS answer: ledger sessions, not artifacts. With the relay-vs-entitlement contrast.2026-07-29
SVG, Rust and Elm: the security gaps illustrationOne diagram that follows a single SVG file from source to base64 to the browser, through an Elm client, TLS, Cloudflare, Xano and a Rust service, two TLS pipelines, JVM, iPaaS and Wasm stacks, and VM, Docker and Kubernetes isolation — with 31 numbered gaps and their fixes, a second illustration of browser, machine and agent callers, the assumptions that break as a system adds commerce, goes global and becomes AI-legible, how Rust keeps an SVG renderer memory-safe and what it still leaves to limits, how to make an SVG tell a model what it shows a person, and a list of known foot guns.2026-10-19
Design for Secure Revenue ProjectionSecurity as a designed component of the revenue signal path: how conversion values, predicted lifetime value and audiences leave a store's own record for Google, Klaviyo and other channels, what the security component checks at each hop, its states and failure modes, what is built and tested today, and what it costs.2026-10-24
Consent, Cookies & Preferences — User GuideThe consent banner, cookie preferences, reset, Do Not Sell vs consent, and the audit trail.2026-07-09
CRM Sync — Migration Guide: CSV & Legacy Tools → Connected StreamsFor: Marketing ops, analytics teams, and CRM administrators planning the transition Date: 2026-05-182026-05-26
Agency → Client Deploy HandoffChecklist + Interactive Key Rotation ceremony. This document is the normative handoff procedure for transferring a deployed CRM Sync / headless commerce stack from the implement…2026-06-12
File System Agnostic PublishingShip the Webflow design as a WordPress theme (Udesly or Pinegrow) or on EmDash/Astro — the Shopify Web Components block and CRM Sync embeds carry across verbatim.2026-09-10
How to capture a HAR file — a plain-language guideA HAR file is a recording of every conversation your browser had with a website. This explains what one is, how to capture a useful one in Chrome, Edge, Firefox or Safari, the single setting most people miss, how to check what is inside before you sh2026-09-07
CRM Sync — PWA & Native App Commerce Setup ReferenceShip your CRM as an installable PWA and native app (iOS · Android · desktop) on Shopify + Webflow + Xano — with auth, real-time consent, GA4, and agent permissions. Everything you need to get it running, in order.2026-07-06
CRM Sync Setup ReferenceThe full technical reference for the CRM Sync stack. New users: start with the short numbered guide at crm-sync.dev/start — this page is for depth.2026-07-07
Logging and trace fees: what monitoring costs by volumeLog entries and trace spans are the two monitoring lines that grow with traffic rather than with tenants. What Google Cloud Logging, Cloud Trace and Cloud Monitoring charge, what Cloudflare Workers Logs and Traces charge from 1 October 2026, what a fixed-fee Xano plan leaves out, and the four settings that decide the bill before the first invoice does2026-09-16
Marketing was built on the page view. The funnel now pays for the consented login.For: Marketing ops, performance media, and analytics engineering Status: Built (GA4 push + audiences) · Direct Google Ads push pending Ads API credentials Date: 2026-07-07 Depen…2026-07-22
Google turned off the list upload. We were never uploading lists.For: Marketing ops, analytics engineering, and the business analyst who owns segments Status: Plan of record · GA4 pipe built · Live Google push routes via the Data Manager API2026-07-10
Shopify App Requirements Checklist (2026)A comprehensive, downloadable checklist for building, submitting, and maintaining a Shopify App Store app. Based on Shopify's official App Store requirements and the latest plat…2026-05-29
CRM Sync — Shopify App Platform ChangesFor: Product managers, operations teams, and business stakeholders tracking Shopify app compliance Date: 2026-05-182026-05-26
Risk & Liability Brief — The 2026 Client-Side CliffAudience: owners, finance, legal, and engineering leads who carry the downside. As of: 2026-06-21 · Companion to: FORWARD-DEPLOY-AGENTIC-GRAPHQL.md (the fix).2026-06-21
Dawn → Horizon: Agentic Cart FunctionsMove client-side Dawn logic to server-side Functions and the Tool Runner — agent-driveable under an AP2 mandate. Includes the Scripts→Functions map and the dated migration checklist.2026-08-06
Hydrogen or a Bespoke Xano + Cloudflare StackShopify Hydrogen 2026-10 compared with a bespoke Xano + Cloudflare stack: integrations, the Shopify and Google deprecation calendar, sign-in, agent checkout, wallets, apps, 3D and permissions.2026-10-29
REST Is Not GraphQLWhat actually breaks when a Shopify integration moves from REST to GraphQL: the inverted error model, cost-based rate limiting, GID identifiers, cursor pagination, and unequal surface coverage - with the failure mode each produces and an audit checklist.2026-07-27
Shopify and Google sunsets: what is due before 11 November 2026Every Shopify, Google Analytics and Google Ads deprecation dated between 16 September and 11 November 2026, the five topics merchants ask about — native mobile, short-lived tokens, the REST sunset, GraphQL data layers, and GA4 consent and conversions — and whether CRM Sync is exposed to each, with every source linked.2026-09-16
JS Execution Order — Challenge & SolutionConsent fires first: the client-JS execution-order contract and the tests that enforce it.2026-07-09
AI Trust Framework RequirementsTen requirements an AI trust framework must satisfy, why REST integration cannot meet them by default, and nine additive changes that close the gap without rewriting an endpoint.2026-07-27
CRM Sync — Why This Architecture Is SaferFor: Business leaders, compliance officers, and operations teams evaluating CRM Sync Date: 2026-05-182026-05-26
Process Management Guide — Webflow · Xano · Cloudflare · ShopifyFour-platform resilience: layer split, event-driven automation, outage runbook and RACI - now extended with verification evidence, SBOM/CRA obligations and AEO surfaces.2026-07-27
Server-Side Function Tools with AI RunnersThe additive way into an enterprise stack: bounded functions that resolve authority per call, record themselves, and give an AI runner capability without a migration to own.2026-07-27
CRM Sync — UI Component & ID RegistryCanonical naming + delivery model for the storefront UI system (nav, footer, cart, login, search) across design-sync.myshopify.com → crm-sync.dev. One addressable crm- namespace…2026-07-07
Product Taxonomy, GraphQL and the GID RenameCPG planning toward Sunrise 2027: what changes when product identity moves into a typed graph with GID identifiers - the parent/child collision, the silent join breakage, and the five identifiers an item master has to carry.2026-07-28
CRM Sync — Feature SpecificationDocument ID: CRM-FEAT-003 Version: 1.0 Date: 2026-07-06 Status: Published Classification: Public Parent: CRM-FUNC-SPEC-0012026-07-06
Forward-Deploy Guideline — Server-Side GraphQL + Agentic Workflows + Tool RunnerAudience: merchants, app developers, and platform teams planning their Shopify roadmap. Thesis: Shopify's 2025–2026 deprecation cliff retires the client-side / REST / Script-Edi…2026-06-21
CRM Sync — What Traditional CRMs MissFor: Business leaders, investors, and operations teams evaluating CRM Sync against Salesforce, HubSpot, and Klaviyo Date: 2026-05-192026-07-19
Analytics Export via Xano Polling + Worker CronVersion: 1.0 Date: 2026-05-27 Status: Specification2026-05-27
Consent-first tracking and the demotion of page and client dataFour dated platform moves demoted the page view from record to hint. Requirements and risk for the theme, what agentic conversion needs instead, and where the page view is still right — AEO vs SEO.2026-09-10
CRM Sync — Functional SpecificationDocument ID: CRM-SYNC-FUNC-SPEC-001 Version: 1.0 Date: 2026-07-12 Status: Active Classification: Public2026-07-12
CRM Sync — Feature Specification AddendumDocument ID: CRM-FEAT-002 Version: 1.0 Date: 2026-05-17 Status: Draft — Architecture Review Parent: CRM-FUNC-SPEC-001 v1.22026-06-25
AI enabled forms with LLM weighting — one form, many outcomesOne form, many outcomes: the business case against CRM latency, per-contact fees and vendor lock-in, with sprint directives and why a claim's shape decides what an AI can be asked.2026-09-08
Asset Management, Security and AIA media manager's pipeline — metadata and provenance, raster and mesh compression, programmatic resize, and the four places media can live compared on egress.2026-09-20
BYO Shape PipelineBring your own Xano, Kubernetes and LLM to the shape pipeline — the merge contract, the write path, the entitlement gate, and a dependency table where every row is self-serve.2026-09-09
BYO Xano and BigQuery against Google's agent platform: what AI automation costs per callGoogle's agent platform is the faster way to build an AI automation, and its managed layers bill every request. What Conversational Agents, Agent Search, grounding and Agent Runtime charge per call, what the same jobs cost on a bring-your-own Xano and BigQuery stack with Cloudflare Workers AI, where Google is cheaper, and the price changes dated between now and January 20272026-09-16
Claim Provenance — the metadata schemaEvery document here is CC BY 4.0. This defines the metadata that travels with it — what was checked, how it was checked, when, and when it should be checked again.2026-09-04
Compile to update — the estate by seven lifecycle stagesEvery application against the same seven stages: compile, permissions, render, bundle, deploy, version, update. The empty cells are the informative ones.2026-09-07
Consent Resolution on Higher-Order LoadThe five-phase load contract that resolves consent from durable state before any tag loads — portable to any client-side template, device- and browser-agnostic.2026-09-04
Decision ladder — functional and data design spec (hypothetical)A support chatbot that climbs from knowledge-base answers to opening a return, escalates to a person on named conditions, links only attested firmware and deploys only through a locked, human-reviewed workflow. With a test matrix.2026-10-04
Fragments on Any Frontend — One Webflow Source, Every PlatformSections authored once in Webflow mount verbatim on AEM, WordPress, Astro, Next, 11ty, or a Shopify theme — markup travels, behavior never does.2026-08-03
From Plugins to MandatesWhy per-seat pricing taxes the automation you bought it for, what each external DAM, PIM and CRM adds to supply chain risk, and why vendor JSON is the wrong shape for an agent.2026-09-20
Git to Every Surface — the Article PipelineOne markdown commit becomes a Webflow article, a Shopify metaobject, and an AEM Content Fragment — with hashtags as the filter dimension and ALT text carried from the source.2026-08-11
Middleware vs AI ArchitectureWhy a Xano record plus a Cloudflare edge resolves identifier and consent drift that VM-hosted middleware cannot, what a GTIN check digit proves, and where cryptographic trust sits in a Channel Publish QR link.2026-10-17
October 1: script tags, Functions, the cart, the catalog agents read — Globalized Language ISO requirementsWhat server-side consent buys globally: the three-year conversion from browser tags to Consent Mode v2 (September 2023 to March 2027), what Google, Meta and the law require, and why no session-level consent log means no YouTube or Meta retargeting; a real-time consent log, California's Honda and Todd Snyder fines, and the browser opt-out signal from 1 January 2027; business-as-usual data vs an API-reinforced global namespace, from market-prefixed domains to Cloudflare Rules; a retire and adopt checklist; then Shopify's 1 October 2026 script tag deadline, Functions, what is reserved in cart and checkout, the ISO standards of the UCP catalog, and Korea's NICEPAY and consent path.2026-09-30
PIM Anywhere — One Catalog Record, Any FrontendOne live catalog record projected onto any frontend — AEM, Webflow, WordPress, Next — via a two-tag embed; the same record ships to Google through the Merchant API.2026-08-05
Render and Runtime: A Working DictionaryISR, islands, HTMX against Next.js, Liquid, PHP passthrough, Deno against Node, keys against cookies, UAT, adversarial testing and SRI — each defined by the decision it changes.2026-09-20
Shopify / Google Integration on an AEM Scaffold — via Webflow ExportThe Webflow export as the AEM page scaffold, worker embeds as the behavior layer, and the either/or substrate election — beside AEM, never inside it.2026-08-02
The AI ladder: retrieval, adapters, humans, and who holds the keysChallenge and solution for putting AI into commerce without letting it decide what it may not. Definitions of RAG, CRAG, LoRA and human-in-the-loop escalation; when data justifies each rung; and why ADK, Kubernetes/Helm and a Cloudflare higher-order 'helmet' are three different layers — with the mandate as the only way an agent is allowed to act; and what a SOC 2 review — a procedural assessment of how an organisation operates, not a certification — asks of AI transport.2026-09-25
The spec is the source — a writing layer for designers and analystsConfiguration files are the specification. Write the intent in plain language, generate the config, and get the developer and compliance documentation from the same file.2026-09-07
Why Xano + AI + e-commerce is the right runtime as a serviceA runtime is judged by what it holds when nothing is being rendered. The identity path across Shopify OIDC, a worker and Xano; a consent gate that is metered rather than loaded; and why Supabase and Firebase lost on the enforcement point.2026-09-06
CRM Sync — Clean Room Utility & Security RulesVersion: 1.1 — Cloudflare-Native Architecture Date: 2026-05-27 Classification: Internal — Confidential Compliance: GDPR Art. 6/9, CCPA §1798.140, CPRA, UK DPA 2018 Infrastructur…2026-05-27
GUIs when you still ship JavaScript: Webflow, Elm, Javy, Tauri and Rust down to machine codeA field guide to interface options for a stack that keeps its JavaScript and TypeScript: Webflow with TypeScript embeds and Workers side by side, Elm and SVG islands, Shopify Functions compiled from JS with Javy, Rust in the browser through WebAssembly, Tauri around an existing web UI, native Rust GUIs (iced, egui, Slint), and no_std firmware with no GUI at all — compared by what JavaScript remains at runtime and where trust is enforced.2026-10-12
From product.csv to Consented ConversionsGoogle retired the Content API and Amazon now drops conversions with no consent signal. Why a product.csv data layer can no longer feed ads or measurement, how a connected ERP, CRM and PIM replace it, and an eighteen-item checklist with a downloadable test harness.2026-10-19
Consented data layer test harnessEighteen tests that prove a catalog has moved off a product.csv data layer: feeds on current APIs, identifiers joined by key, consent attached to every conversion, and a clean boundary between the PIM and the CRM. Each test is a shell check, an in-app check or a browser check, with the result that counts as a pass.2026-10-19
Hyperscaler vs Distributed: Webflow, Xano and Cloudflare Decision LaddersWhere compute should live, from hyperscalers and GPU neoclouds to edge networks. Opens with task runners, data bindings, and GPUs as a rented place (CoreWeave, Oracle OCI) versus GPU code compiled from Rust to bytecode. Then the frame-budget origin: how game engines already ration the GPU, why C and C++ renderers such as Flash and SVG parsers forced isolation that Rust and Wasm remove, how Shopify Functions already run Wasm as a security boundary inside checkout, and the Rust path for new work: a Webflow page, a Cloudflare compile and a Xano record. Then the strategy: bind before you allocate, with the cost and security case for running distributed data and AI binding before any GPU is allocated. Then incremental knowledge against general-purpose AI: evidence weighting, ranking, and falling back to a larger token model only when the ranked data can't answer. Then context and data streams that scale by direction before intent is tokenized or vectorized. Then why Kubernetes and VMs limit reach but not what a model may weigh, how AWS, Google Cloud and Azure each control data moving between workloads, what an enterprise has to add on top, and policy management as a service: rules authored in Webflow and Xano, enforced by Cloudflare above every cloud, worked through one order that reaches Salesforce and Klaviyo on AWS, SAP or Dynamics on Azure, Google Ads on Google Cloud and a Shopify Function; and one Worker behind any theme, a Webflow export or a Shopify theme through the App Proxy, with an allowlist that mirrors Kakao Pay's registered domains; a sandbox that restricts outside data before it reaches on-prem; and why an AI strategy is not a JVM: security for AI as permissions as architecture, with the stack and the heap as a model for which data and grants may outlive a call; immutable and dynamic data in KV; claims and extras as layered permissions for people; and why a one-domain consent banner such as OneTrust has to fold into the data design that AI services read. Then two decision ladders, for orchestration and for AI binding, across Webflow, Cloudflare and Xano, plus what each rung does to residency, latency, cost, audit scope and failure modes in enterprise infrastructure.2026-10-20
CRM Sync — Event-Driven Integration SpecVersion: 1.0 Date: 2026-05-27 Status: Specification Replaces: Cron-only polling for external integrations2026-07-22
Webflow App Requirements Checklist (2026)A comprehensive, downloadable checklist for building, submitting, and maintaining a Webflow Marketplace app. Based on Webflow's official Marketplace guidelines and the latest pl…2026-05-29
Design HelmetThe Helmet is our way of drawing the logo once so that every site colours it automatically to match the brand — you never re-export it, and you never touch code.
Safe SVG for Webflow and UIkitAn img is sandboxed; inlining spends that sandbox for stylability. An allow-list sanitiser buys it back — tested against twelve vectors, with GSAP and Lottie separated by who supplies the program.2026-09-20
The Webflow App Stack — Vite + TypeScript Monorepo, with 11ty/Vue/Svelte IslandsThe modern hybrid-app scaffold: pnpm monorepo, Vite + TS extension, CF Worker, shared types end-to-end — plus 11ty/Astro islands for the site and the Turbopack risk, defined.2026-07-29